Category Archives: Blog
PHI & ePHI Data
Securing PHI and ePHI Organizations create and exchange enormous amounts of sensitive information every day. This is certainly true of government agencies, and of course, healthcare organizations. In healthcare, patient records move through electronic health records, laboratory systems, billing applications, email, cloud platforms, collaboration tools, medical devices, data warehouses, file shares, backups, and third-party applications. […]
What Anthropic's Mythos Means for Security
Can Your Organization Patch at AI Speed? Anthropic’s Claude Mythos Preview is a powerful AI model designed to identify and exploit software vulnerabilities at a speed and scale never seen before. Anthropic has stated that Mythos has already found thousands of high-severity vulnerabilities, including flaws in every major operating system and major web browser. Anvaya […]
Using AI in Penetration Testing
Using AI in Penetration Testing: The Future Is Already Here Artificial Intelligence is no longer a futuristic concept in cybersecurity. It’s already embedded inside enterprise networks, security tooling, development pipelines, and increasingly, inside real-world attacks. See how the experts are adapting and using AI in penetration testing If you’re not actively thinking about how AI […]
How to Secure Your Application in 2026
How to Secure Your Application in 2026 Modern businesses rely more and more on software every day. Even then, more and more companies are asking the same critical question: How do you truly secure your application? Application Security in 2026 Requires a Shift in Thinking Entire businesses now run on software, and the security of […]
How to Choose the Right Penetration Test Partner
Beyond the Scan: How to Choose the Right Penetration Testing Partner Everyone needs to know how to chose the right penetration test partner. Engaging an independent Vulnerability Assessment (VA) and Penetration Testing (PT) consultant is a strategic decision that directly impacts an organization’s security posture. Drawing from real-world practitioner experience, this blog breaks down what […]
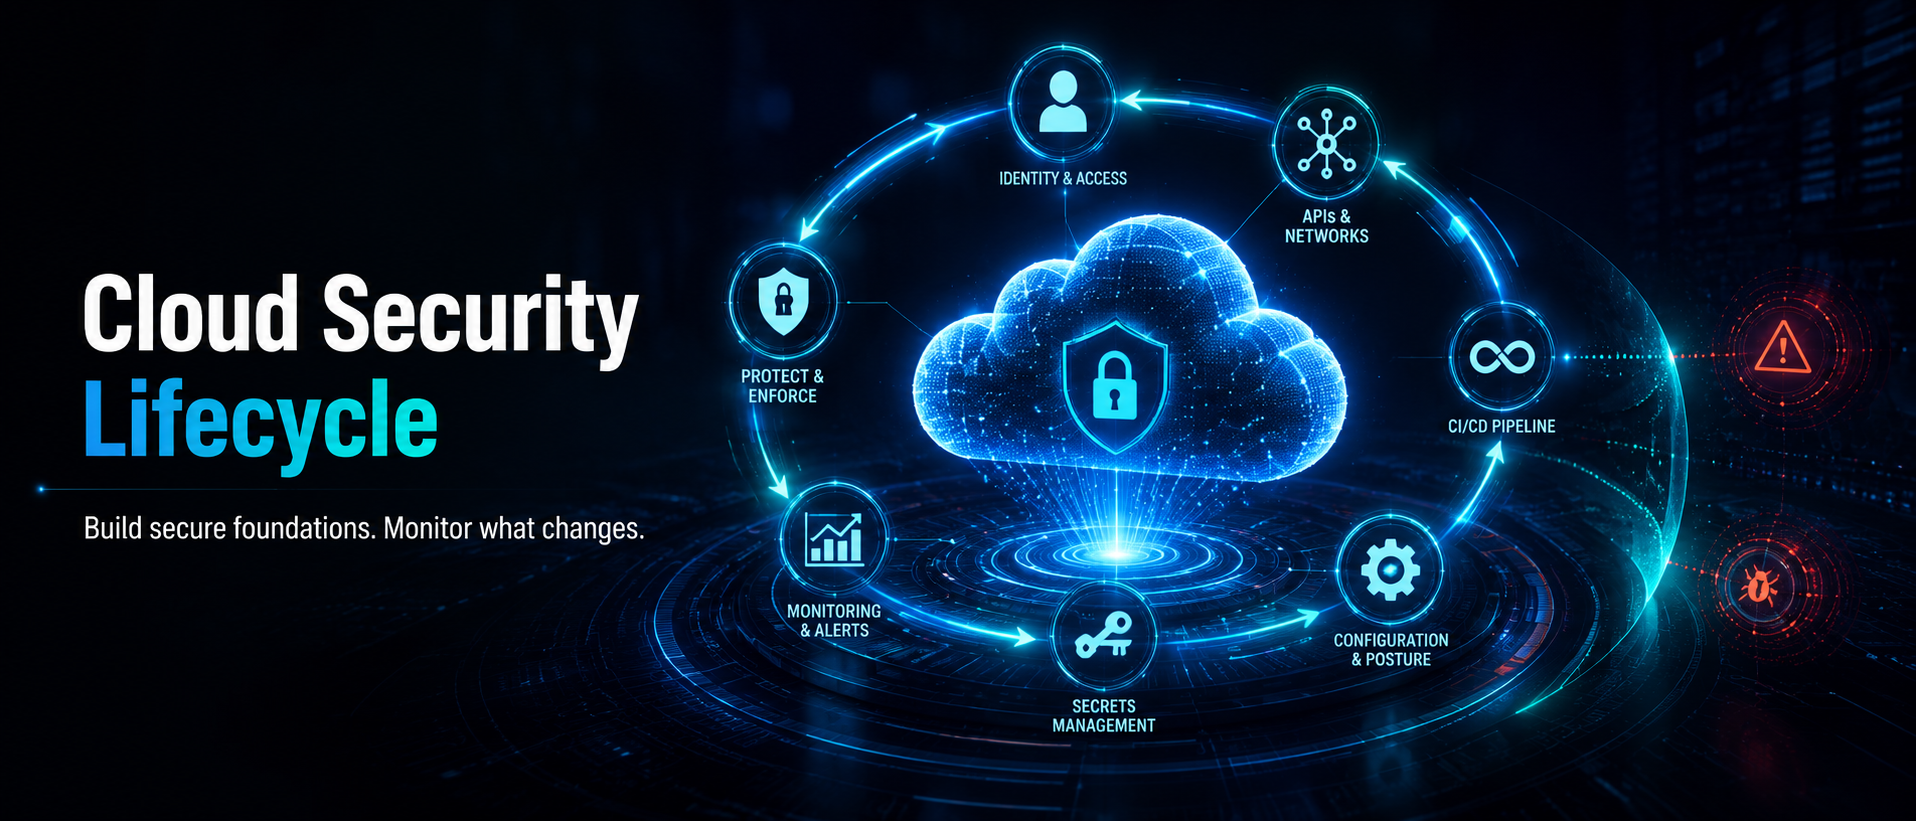
Cloud Security Lifecycle Best Practices by Anvaya
Cloud security lifecycle best practices and Anvaya’s practical take on protecting what changes every day Cloud security matters because the cloud changes faster than most security programs can keep up with. The cloud is a living environment made of identity, APIs, automation, managed services, short-lived workloads, third-party integrations, and constant deployments. That velocity is exactly […]
The Purpose of Threat Modeling
From Understanding to Anticipation: The Purpose of Threat Modeling The primary goal of Threat Modeling is to anticipate and mitigate attack vectors, vulnerabilities, and threats before they can be exploited. This structured approach aligns closely with federal guidance, including NIST SP 800-30 “Guide for Conducting Risk Assessments” and NIST SP 800-154 “Guide to Data-Centric Threat […]
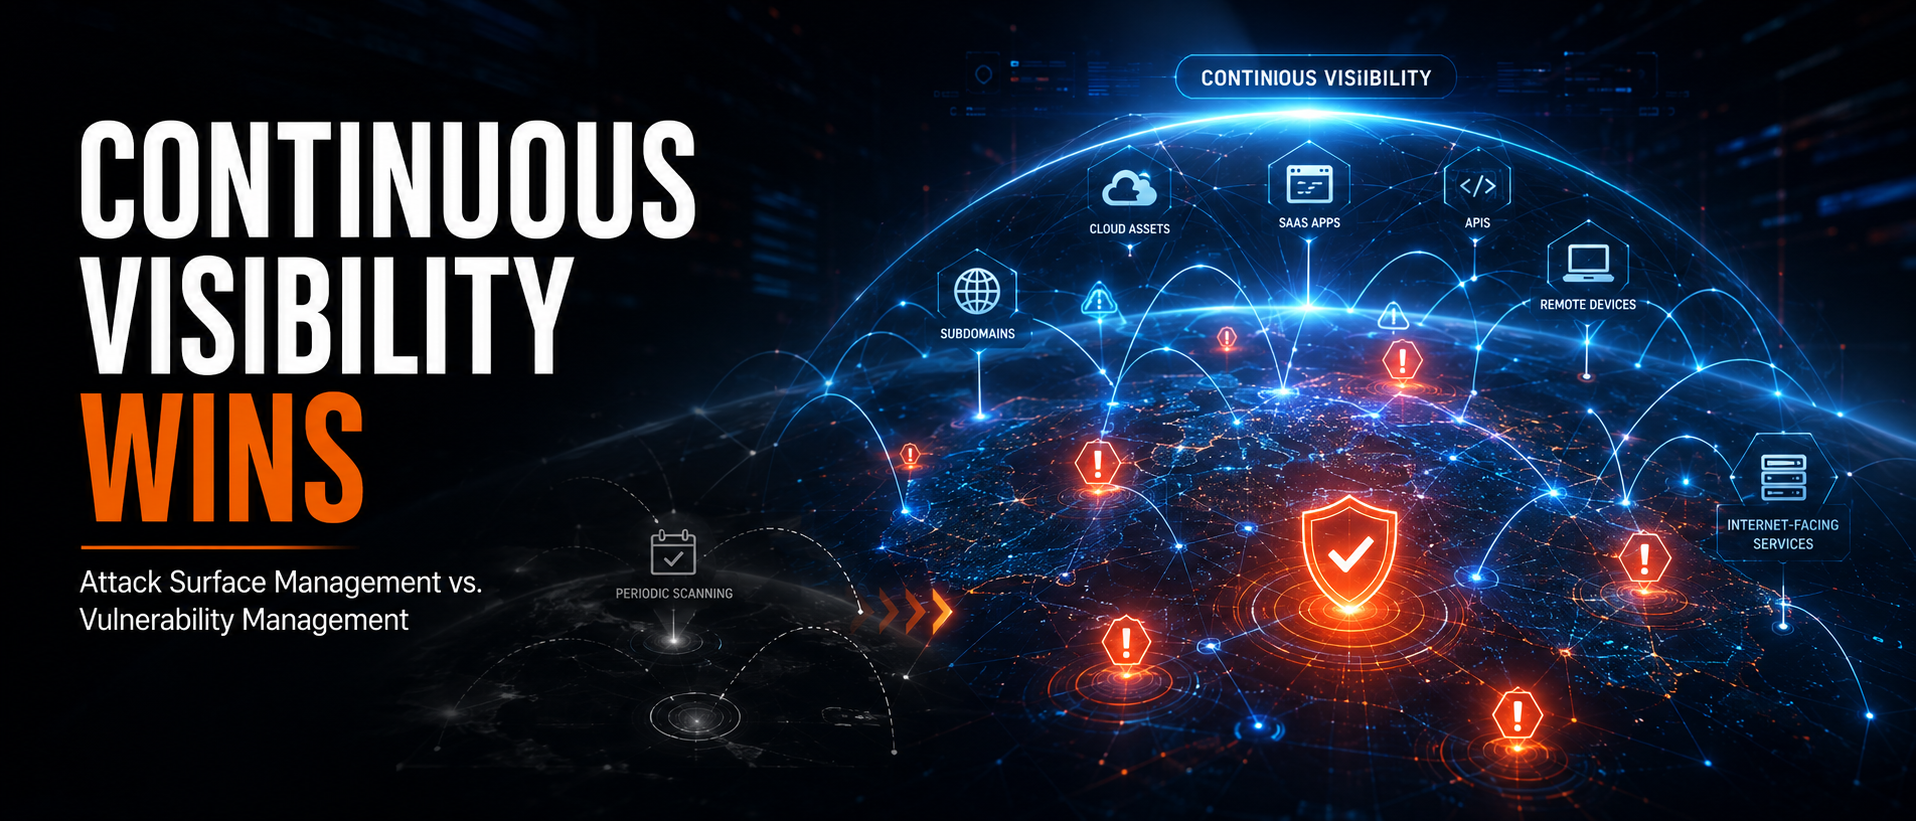
Attack Surface Management vs. Vulnerability Management
From Periodic Scanning to Continuous Visibility For years, organizations relied on traditional vulnerability management (VM) — scanning known assets, identifying weaknesses, and patching them. While VM remains essential, today’s cloud-driven, interconnected environments have dramatically changed the security landscape. In this blog we discuss attack surface management vs vulnerability management Modern enterprises aren’t defending static networks […]
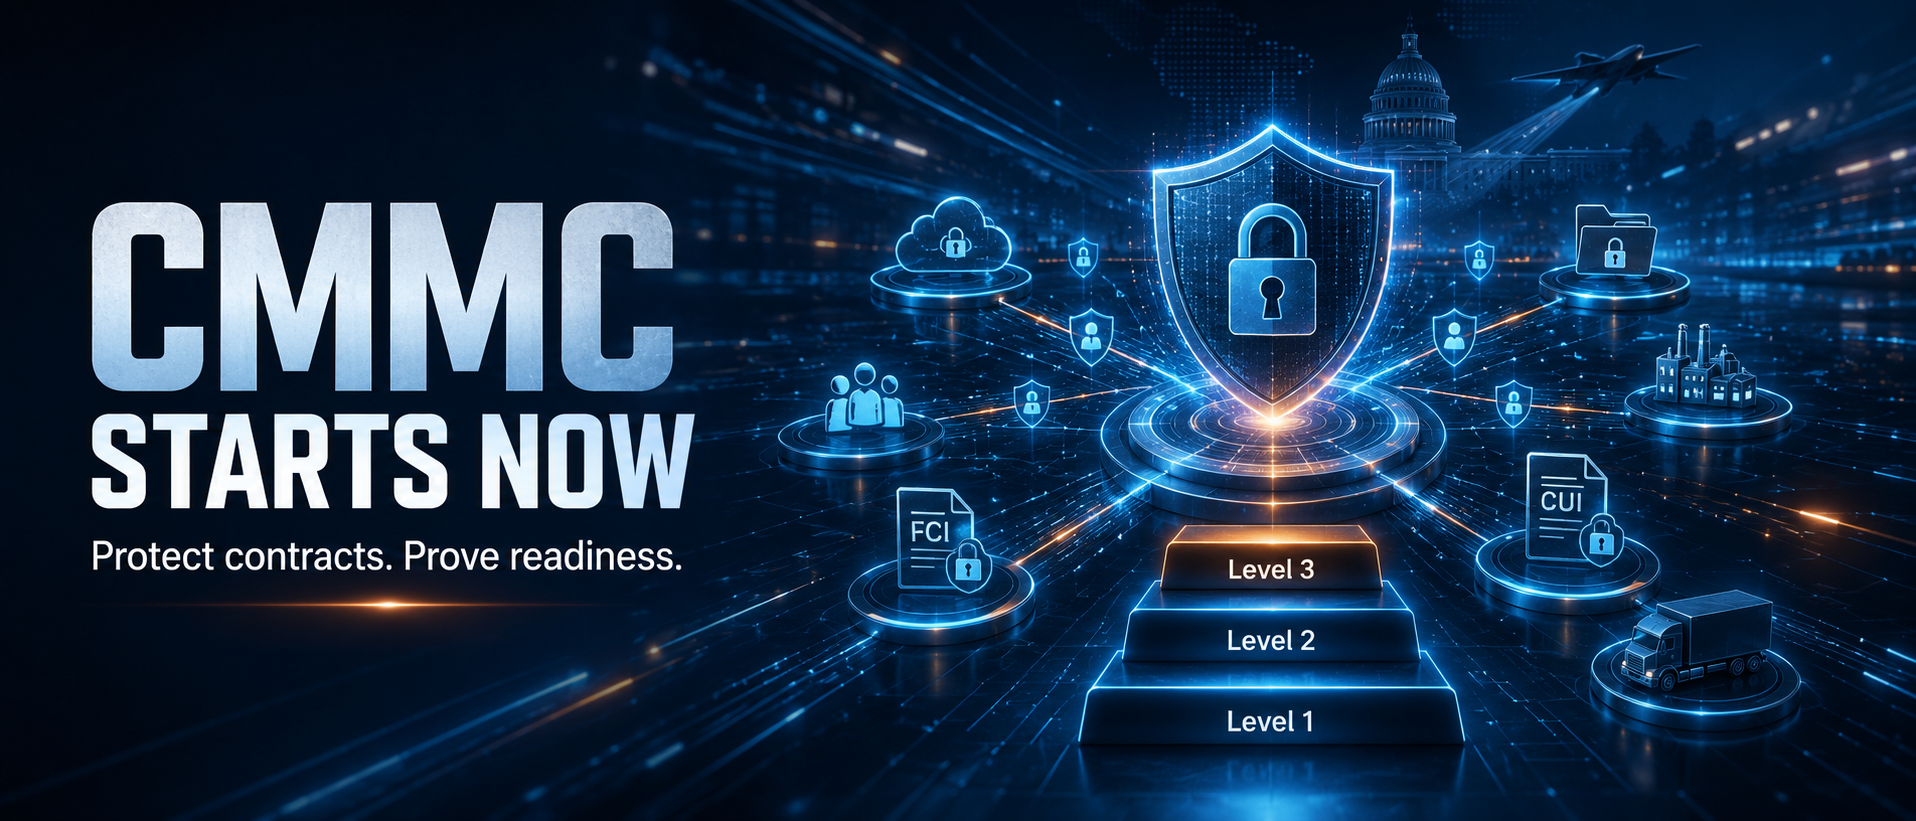
CMMC - Protecting the Future of Your DoD Contracts Starts Now
Why CMMC Matters to You If your organization is part of the Defense Industrial Base (DIB), cybersecurity is no longer just a best practice – it’s going to be a contractual requirement. The Cybersecurity Maturity Model Certification (CMMC) ensures that every company handling Federal Contract Information (FCI) or Controlled Unclassified Information (CUI) meets strict data […]
No results found.
There are no results with this criteria. Try changing your search.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.